Skip to content
Skip to content

Practical AI project guide · By Yes AI

How to write an AI use policy for your staff

Published 6 min read

An AI use policy tells staff which tools they may use, what information can go into them and when a person must check the result. The National AI Centre publishes a free template, and this guide covers the decisions you need to make before you fill it in. Keep the finished policy short enough that staff will read it.

Quick answer

A staff AI use policy should state what AI can and cannot be used for, which tools and account types are approved, what information staff may enter, when a person must review output before it is used, who approves new tools and higher-risk uses, how to report problems or misuse, and when the policy will be reviewed. Start from the National AI Centre's template, test the draft with the staff who will use it and name a senior owner.

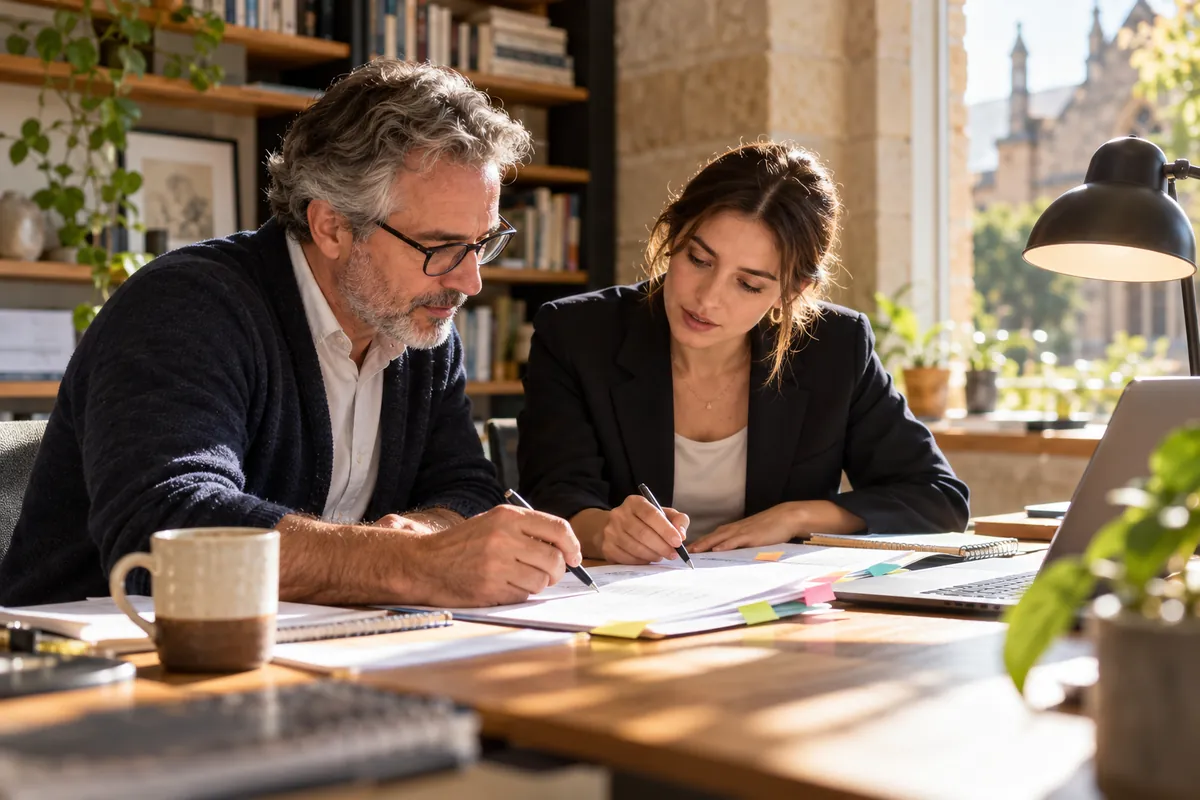
Two colleagues at an Adelaide office desk marking up a printed draft policy with pens
Testing the draft with the staff who will use it shows which rules are unclear.

What should the policy cover?

The National AI Centre's guidance lists the points a policy should make clear before it is finalised, and they work as a table of contents. Its template adds core principles, expected behaviours, roles and responsibilities, governance and approval points, and monitoring and review guidance. Write in the terms your staff already use, and match roles to the governance structure you already have, so the policy describes how your business actually works.

  • What AI can and cannot be used for.
  • Who approves higher-risk use cases.
  • What data staff can put into tools.
  • When staff need to oversee AI use.
  • How staff report issues or misuse.
  • When the policy will be reviewed.

Which tools and accounts are approved?

Name the approved tools in an appendix you can update without rewriting the policy, and state the account type for each. A business plan managed by the company can carry different data terms and admin controls from a free or personal account of the same product, so the account matters as much as the brand. Say whether staff may use AI features built into software the business already licenses, and how they request a tool that is not on the list. If you have not yet found out what staff already use, do that first, or the approved list will not match what happens at work.

What information can staff put into AI tools?

This is the rule staff most need, so make it concrete. Group information into a few types your staff recognise and give a rule for each type and each class of tool. The OAIC's best-practice recommendation is that organisations do not enter personal information, and particularly sensitive information, into publicly available generative AI tools. It also notes that privacy obligations apply to personal information put into an AI system and to outputs that contain it, so the same care applies to what comes out. Cover passwords, access keys and commercially confidential material too. Privacy law may not reach them, and exposing them still causes real harm.

When must a person check the output?

Set review rules by consequence. Internal brainstorming may need no review. Anything sent to a client, published, used in a quote, contract or financial figure, or used in a decision about a person should be checked by someone accountable for the result. Say what checking means: confirming facts, figures and references against the source. If your business tells clients when AI has been used in their work, state when and how. The OAIC also expects organisations to update privacy policies and notifications with clear information about their use of AI, including identifying public-facing tools such as chatbots.

Who approves new tools and higher-risk uses?

Name one senior owner for the policy. The National AI Centre's foundations guidance asks for a senior leader as the overall AI governance owner, with enough authority and understanding to oversee all AI use. Then set a simple approval route: tools on the approved list need no further approval for their listed uses, a new tool needs the owner's sign-off, and any use that makes or informs decisions about customers or staff needs a documented risk check first. The risk screening template published with the guidance is a reasonable gate for that last step.

How do staff report a problem?

Give one reporting route, such as a named person or a shared mailbox, and say what to report: wrong output that reached a client, personal or confidential information entered into an unapproved tool, a tool behaving unexpectedly or someone using AI against the policy. Make it clear that prompt reporting is expected and will not be punished in itself. Where personal information may have been exposed, the report should reach whoever handles privacy incidents, because the implementation guidance reminds organisations to meet data breach reporting requirements such as the OAIC's Notifiable Data Breaches scheme.

How do you get staff to follow it?

Write it with the people who will use it. The National AI Centre recommends testing the draft with the people who will use, review or oversee it, and its readiness guidance notes that employers have obligations to consult under workplace and work health and safety laws. Run a short session at launch using real tasks from your business, publish the approved tool list where staff work and set a review date. Review sooner if a major tool changes its terms, a new use is proposed or an incident shows a gap.

Example data rules to adapt for your own business

Information typeFree or personal AI accountApproved business AI toolNotes
Published material, such as website copyAllowedAllowedCheck facts before reuse
Internal procedures with no client detailsNot allowedAllowedKeep the source document as the reference
Client names, contact details and job recordsNot allowedAllowed for approved tasks onlyRemove details the task does not need
Health, financial or other sensitive personal informationNot allowedOnly for uses approved after a privacy checkOAIC best practice: keep it out of public generative AI tools
Passwords, access keys and codesNeverNeverReport any exposure straight away
Tenders, pricing and other confidential commercial materialNot allowedAllowed if the tool's terms suitCheck contract confidentiality clauses first

Practical checklist

  • The policy names a senior owner and a review date.
  • Approved tools are listed with the account type for each, in an appendix that can be updated.
  • The data rules give a clear answer for each type of information staff handle.
  • Review rules say which outputs a person must check before use and what checking means.
  • The approval route for new tools and higher-risk uses is written down.
  • There is one reporting route for problems, linked to the privacy incident process.
  • Staff who will use the policy have reviewed the draft and been consulted.

Common questions

Does a business with 10 staff need a written AI policy?

If staff use AI tools for work, a short written policy is worth having at any size. It settles what information can go into which tools, which is the question most likely to cause a privacy or confidentiality problem. For a small team, one or two pages plus an approved tool list is enough to start.

Should the policy name specific products?

Put them in an appendix. Products, plans and terms change often, and an appendix can be updated by the policy owner without a full review. Keep the body of the policy about principles, data rules, review, approval and reporting, which change less often.

Can staff use AI on their own phones for work?

Decide this explicitly. The risk is less about the device and more about the account and the information. If staff use a personal account on a phone for work tasks, the business has no admin control over that account. One workable rule is to allow approved business apps on personal phones and prohibit work information in personal AI accounts.

Do we have to tell clients we use AI?

Check your contracts, professional obligations and privacy policy. The OAIC expects organisations to update privacy policies and notifications with clear information about their use of AI, including identifying public-facing tools such as chatbots. Beyond that, decide as a business when clients are told, write it into the policy and apply it consistently. This is general guidance; seek advice for your profession.

How often should the policy be reviewed?

Set a fixed review date when you publish it, and review earlier when something changes: a new tool is proposed, an approved tool changes its data terms, the law changes or an incident shows a gap. The National AI Centre's checklist treats the review date as one of the points every policy must state.

Sources and further reading

Continue planning

Turn the project decision into an agreed next step

Describe the business process, project stage and decision you need to make. We can discuss scope, evidence and who should own the next step. Keep confidential records, credentials and sensitive commercial details out of this enquiry.